
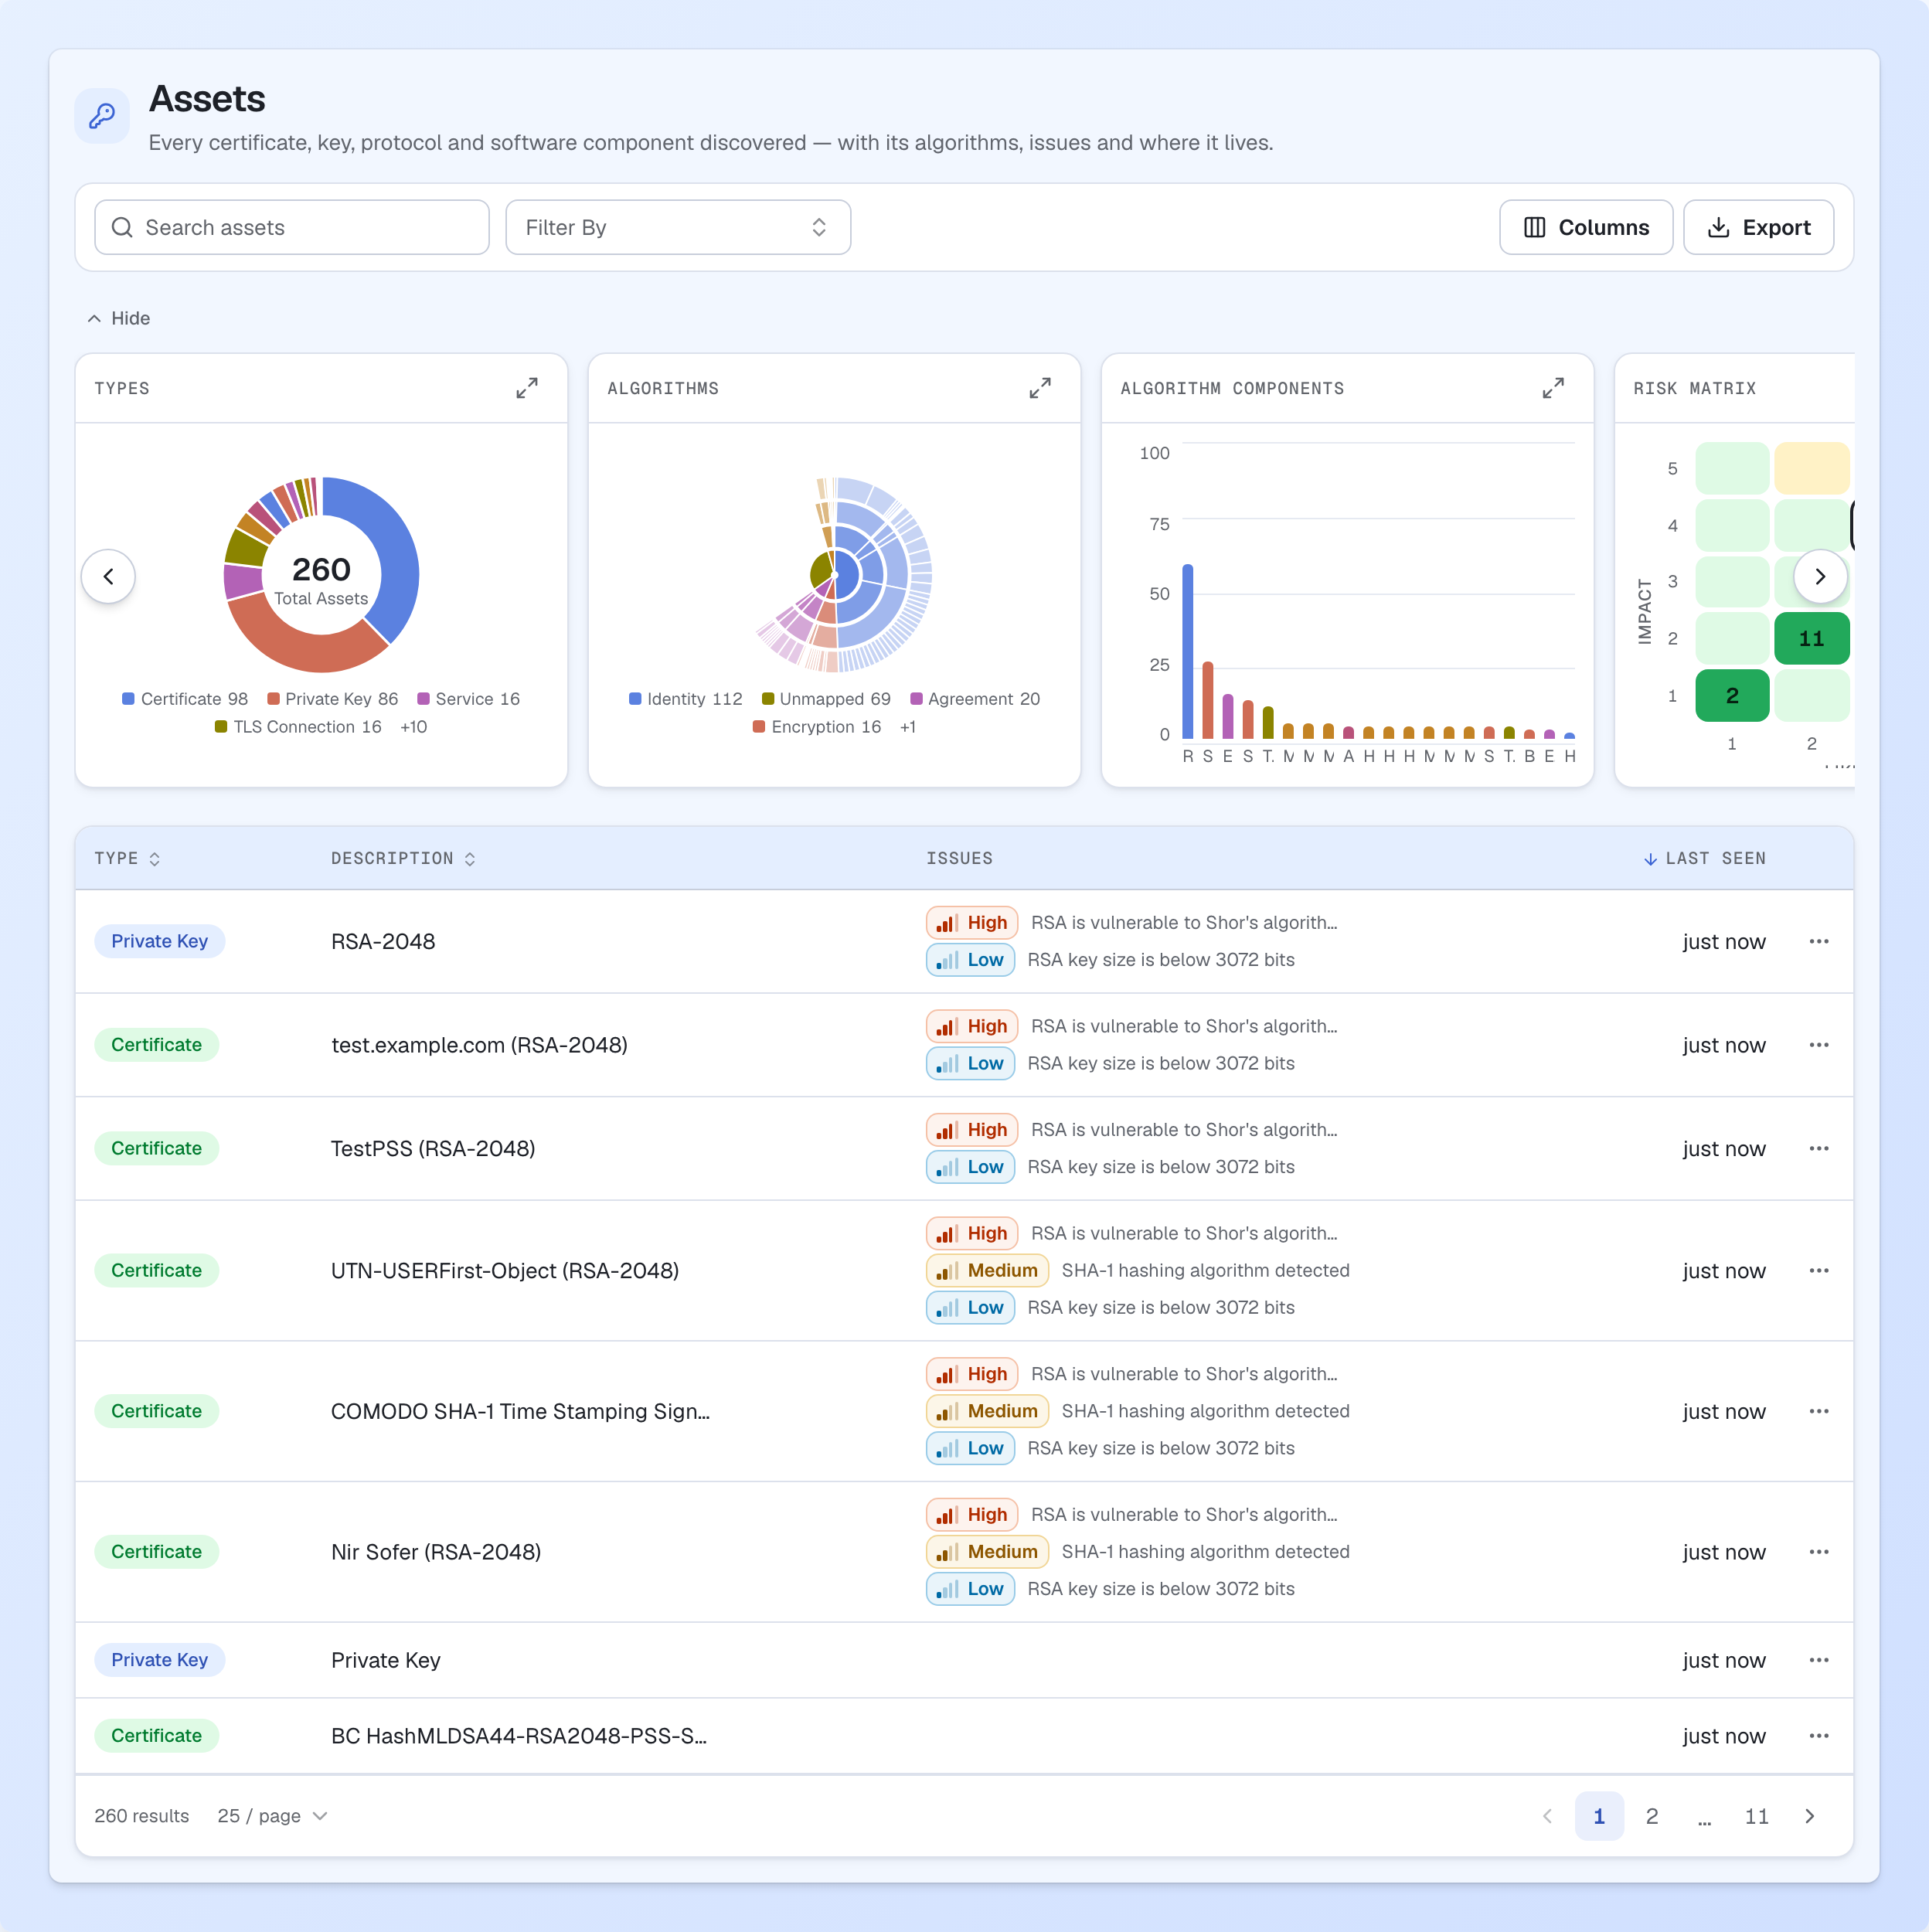
Cryptographic discovery is the process of identifying cryptographic assets and evidence of cryptographic use in an environment. Findings can include certificates, keys, algorithms, protocols, and the software or services associated with them.
How is it different from a certificate inventory?
A certificate inventory focuses on certificates and properties such as issuer, validity, and key algorithm. A broader cryptographic inventory also considers other material and usage context. A certificate inventory can be an important part of that picture without representing all of it. The broader practice is often called cryptographic asset discovery and inventory; see what CADI means and how it differs from certificate lifecycle management.
What makes a finding useful?
An asset record becomes more actionable when it includes evidence of where it was observed and relationships that help explain its use. Technical teams can then investigate the finding, establish who owns the affected system, and determine whether action is needed.
Discovery also has limits. Access restrictions, scan scope, encrypted content, and systems outside the assessment can create gaps. A useful report explains what was observed and preserves the distinction between observations and conclusions.
How does discovery support post-quantum planning?
An inventory gives teams a baseline for investigating cryptographic dependencies. They can combine that evidence with data sensitivity, system ownership, and supplier roadmaps to plan migration work. The inventory is an input to that work, not proof that a system is ready for a cryptographic change.